DFARS Clauses Guide | CMMC and NIST 800-171
DFARS · NIST 800-171 · CMMC Level 2

Know exactly which DFARS clauses you signed, and what they obligate you to do.

If your contract includes 252.204-7012 and your systems touch CUI, you're already on the hook for 110 controls, 72-hour breach reporting, and mandatory flowdowns. Read the clauses correctly before an assessor (or a breach) does it for you.

FREE DOWNLOAD · Clause-by-clause breakdown · Obligations · Flowdowns · Evidence
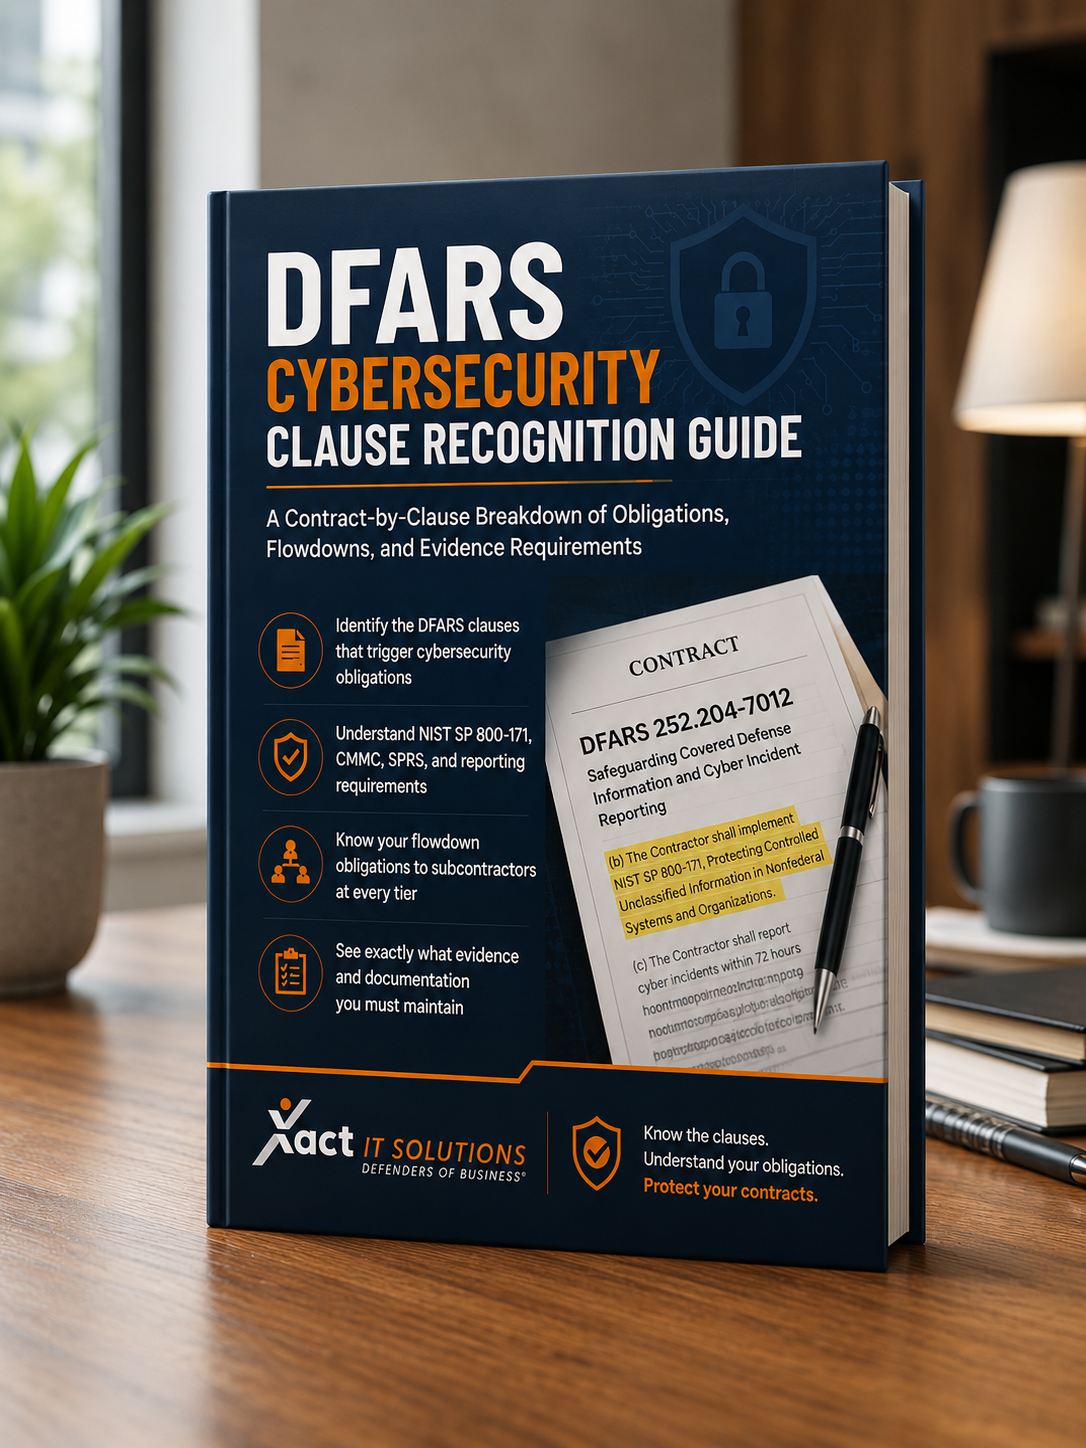
DFARS Cybersecurity Clause Recognition Guide
CMMC Program Update

As of September 2026, the Department has suspended the transition to CMMC Phase II while it reviews the program. Phase I requirements and existing DFARS and NIST SP 800-171 obligations remain in effect. Contractors should follow the requirements written into each solicitation, contract, and subcontract. The suspension applies to the Phase II transition, not the entire CMMC program.

Read the official announcement
The clause was there the whole time

DFARS clauses aren't boilerplate. They're enforceable obligations.

DoD uses DFARS clauses to push cybersecurity requirements down through the supply chain. When one appears in your contract (or gets flowed down from a prime), you've accepted the obligation, whether you read it or not.

  • 7012Adequate security, now. Not a future goal. The moment you sign and your system touches covered defense information, the 110 NIST 800-171 controls are required.
  • FCAFalse Claims Act exposure. Knowingly making inaccurate representations about contractual cybersecurity compliance can create False Claims Act exposure. The risk depends on the contract requirements, the representations made, and the organization's actual implementation.
  • SUBSubcontractors inherit it. When a prime flows a clause down, you accept the same obligations, often discovered mid-performance.
Recognize these on sight

Five DFARS Clauses Defense Contractors Should Recognize

A single contract can include several cybersecurity clauses. Review the solicitation, contract, task order, and applicable flowdowns to identify which clauses apply and what each one requires.

252.204-7012
Safeguarding Covered Defense Information & Cyber Incident Reporting

This clause requires contractors to provide adequate security for covered contractor information systems that process, store, or transmit covered defense information. It includes the applicable NIST SP 800-171 security requirements, 72-hour cyber incident reporting, evidence-preservation obligations, and required flowdowns to subcontractors that handle covered defense information. Confirm the applicable NIST SP 800-171 version from the solicitation, contract, or contracting officer.

Flowdown: Mandatory
252.204-7019
Notice of NIST SP 800-171 DoD Assessment

This provision requires a current NIST SP 800-171 DoD Assessment for each covered contractor information system relevant to the offer. The summary-level score must be posted in SPRS before an applicable award. An assessment is generally current for up to three years unless the solicitation specifies a shorter period.

Pre-Award Gate
252.204-7020
NIST SP 800-171 DoD Assessment Requirements

This clause gives the Government the right to conduct a Medium or High NIST SP 800-171 DoD Assessment and requires contractor cooperation, including access to applicable facilities, systems, personnel, and documentation. It also includes subcontractor assessment and flowdown requirements.

Government Assessment
252.204-7021
CMMC Requirements

This clause identifies the CMMC status required for the contract. Level 2 may require either a self-assessment or a C3PAO assessment, depending on the solicitation or contract. It also includes SPRS reporting, annual affirmation, continuous compliance, and flowdown requirements. Contractors must follow the exact CMMC status written into the applicable solicitation, contract, or subcontract.

Flowdown: Contract-Specific CMMC Status
252.239-7010
Cloud Computing Services

This clause applies when the Government acquires cloud computing services. Separately, DFARS 252.204-7012 requires an external cloud service provider that processes, stores, or transmits covered defense information to meet security requirements equivalent to the FedRAMP Moderate baseline and applicable incident-reporting obligations. Confirm the contract scope and applicable clauses before selecting a cloud provider.

Cloud Services: Verify Contract Scope
STACK ↯

These clauses can appear together, but they do not create identical obligations. A contract may combine safeguarding, SPRS, Government assessment, CMMC status, cloud-service, and flowdown requirements. The guide maps each clause to the specific responsibilities and evidence it may require.
Where contractors get it wrong

Five mistakes that turn into assessment findings

Each of these is common, avoidable, and exactly what a Medium or High assessor will look for.

Treating 7012 as a future obligation

When DFARS 252.204-7012 applies, the safeguarding and reporting obligations are contractual requirements, not future readiness goals. Contractors should determine which systems process, store, or transmit covered defense information and document how the applicable requirements are implemented.

Missing a flowed-down clause

Flowdown requirements may appear in a subcontract, purchase order, attachment, incorporated clause, or prime-contractor template. Before handling covered defense information, verify the applicable clauses, security requirements, reporting responsibilities, and subcontractor obligations.

An SPRS score with no documentation

A score without a dated self-assessment, SSP, and POA&M behind it is a significant finding waiting to happen under 7020.

Scoping the boundary wrong

Too broad pulls in systems that needn't carry 800-171 obligations. Too narrow leaves out systems that legitimately process CUI. Your scope must be documented and defensible.

Ignoring the 72-hour window

If your incident response plan doesn't name DIBNet, assign an owner, and define evidence preservation, you'll miss the reporting window under pressure.

Want the fixes for all five?

The guide pairs each clause with the documentation and evidence that keeps it from becoming a finding.

Get my free guide →
The lead magnet

The DFARS Cybersecurity Clause Recognition Guide

A contract-by-clause breakdown of obligations, flowdowns, and evidence requirements, built for the people doing the actual contract work. Inside:

  • ›Five important clauses to recognize: 252.204-7012, 252.204-7019, 252.204-7020, 252.204-7021, and 252.239-7010
  • ›What each clause actually requires, in plain language
  • ›Flowdown rules so subcontractors know what they've inherited
  • ›The evidence artifacts each clause drives: SSP, POA&M, SPRS, incident response
  • ›A six-step compliance trigger map to run against your active contracts
Download the DFARS breakdown →
Get your copy

Send me the Clause Recognition Guide

Drop your details and we'll send the full clause-by-clause breakdown straight to your inbox: obligations, flowdowns, and the evidence each clause requires.

NO SPAM · The guide, then occasional CMMC insights. Unsubscribe anytime.

Know what you signed. Implement what you owe.

Claim the guide →
Official References

CMMC requirements and DFARS clauses continue to evolve. Verify requirements against your current solicitation, contract, or subcontract and official DoD, Acquisition.gov, and CMMC program guidance. This resource is educational and is not legal advice.

CMMC and DFARS guidance for the defense industrial base. Helping contractors and subcontractors read what they signed and implement what they owe.

Contact

© Xact Cybersecurity. All rights reserved. CMMC requirements and DFARS clauses continue to evolve. Verify requirements against your current solicitation, contract, or subcontract and official DoD, Acquisition.gov, and CMMC program guidance. This resource is educational and is not legal advice.